Datasheet | How Check Point WAF Pre-emptively Blocked “PHP2Shell”
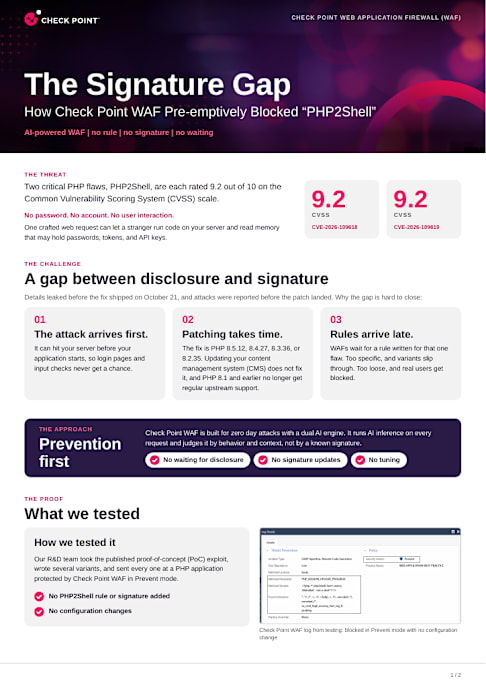
When a zero day like PHP2Shell appears, Check Point’s dual AI engine takes a prevention-first approach, no rules to write, no updates, no waiting. Just preemptive prevention.
CHECK POINT WEB APPLICATION FIREWALL (WAF)
How Check Point WAF Pre-emptively Blocked “PHP2Shell” AI-powered WAF | no rule | no signature | no waiting
THE THREAT
Two critical PHP flaws, PHP2Shell (CVE-2026-109618 and CVE-2026-109619), are each rated 9.2 out of 10 on the CVSS scale.
No password. No account. No user interaction.
One crafted web request can let a stranger run code on your server and read memory that may hold passwords, tokens, and API keys.
9.2 CVSS
CVE-2026-109618
9.2 CVSS
CVE-2026-109619
THE CHALLENGE
A gap between disclosure and signature Details leaked before the fix shipped on October 21, and attacks were reported before the patch landed. Why the gap is hard to close:
01 The attack arrives first. It can hit your server before your application starts, so login pages and input checks never get a chance.
02 Patching takes time. The fix is PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35. Updating your content management system (CMS) does not fix it, and PHP 8.1 and earlier no longer get regular upstream support.
03 Rules arrive late. WAFs wait for a rule written for that one flaw. Too specific, and variants slip through. Too loose, and real users get blocked.
THE APPROACH
Prevention first
Check Point WAF is built for zero day attacks with a dual AI engine. It runs AI inference on every request and judges it by behavior and context, not by a known signature.
No waiting for disclosure No signature updates No tuning
THE PROOF
What we tested How we tested it Our R&D team took the published proof-of-concept (PoC) exploit, wrote several variants, and sent every one at a PHP application protected by Check Point WAF in Prevent mode.
No PHP2Shell rule or signature added
No configuration changes
Check Point WAF log from testing: blocked in Prevent mode with no configuration change
1 / 2
PHP2SHELL · CHECK POINT WAF
THE PROOF
What we saw in the wild
Oct. 21, 2026 First PHP2Shell attack we observed
~10% Attack attempts against approximately 10% of our tenants: blocked without any security patch
PoC Published proof-of-concept (PoC) exploit: preemptively blocked with no configuration change
WHY CHECK POINT WAF WORKED
Two AI engines, one decision Attack Indicator Analysis Trained on millions of malicious and legitimate requests. It picks up subtle attack patterns and new variants, even when no one has written a rule for that flaw. +
Context Analysis Engines Four engines learn what normal looks like for your app. This keeps legitimate requests from being blocked. Blocks only the requests that do not fit.
User Behavior Crowd Behavior Trusted Users
Application Content
What customers experienced No emergency rule tuning No configuration changes No waiting for a PHP2Shell rule
Automatic, preemptive protection against PHP2Shell exploit attempts, in testing and in live attacks, with no manual intervention. Not our first zero day: the same engines preemptively blocked React2Shell, Log4Shell, Spring4Shell, and MOVEit without signatures.
Recommended actions 1 Patch to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, then restart PHP-
FPM or Apache
2 Place internet-facing PHP apps behind Check Point WAF in Prevent mode
3 Enable IPS, rate limiting, and DDoS protection
4 Monitor file-upload endpoints and multipart traffic
5 Isolate end-of-life PHP (8.1 and earlier) and PHP embedded in appliances
One platform for web, API, and GenAI
The next zero day won’t wait. Be ready with AI-powered WAF Learn more
2 / 2
Automatic API discovery and schema enforcement
Bot prevention and rate limiting
Built-in CDN with WAF as a Service
File security via ThreatCloud AI reputation
IPS and Layer 7 DDoS protection
GenAI app protection (prompt injection, data leakage)
WAF-as-a-Service, deployed in minutes
https://www.checkpoint.com/resources/items/ebook-are-your-applications-ready-for-minus-zero-day-attacks