Datasheet | Secure Access for OT Contractors
Discover how Enterprise Browser supports secure access for contractors maintaining Operational Technology environments.
Secure OT Contractor Access: Choose the Right Model
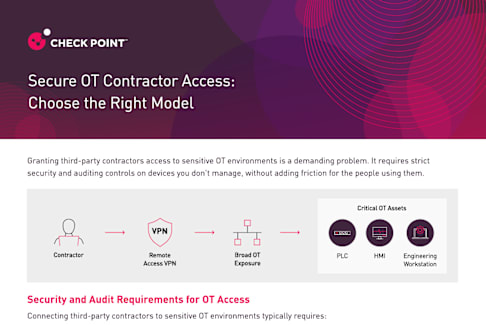
Granting third-party contractors access to sensitive OT environments is a demanding problem. It requires strict
security and auditing controls on devices you don't manage, without adding friction for the people using them.
Critical OT Assets
Contractor Broad OT Exposure
Remote Access VPN
Security and Audit Requirements for OT Access Connecting third-party contractors to sensitive OT environments typically requires:
Strong multi-factor authentication (MFA)
Device posture validation to verify devices meet minimum security standards before granting access
Data control and isolation to prevent sensitive data from being downloaded to the device
Granular, zero-trust access that is restricted to a specific application or jump server, never the broader network
Time-limited connectivity with a built-in workflow that lets contractors request access for a specific task or window
Complete audit and visibility including full session recording
Secure OT Access for Unmanaged Devices Contractors typically work from an unmanaged laptop, often administered by a third-party IT provider. For that reason, secure access must be non-intrusive, deployable, and usable on devices the organization doesn't control.
Two approaches fit this need:
Choose Enterprise Browser when you need full session governance via a jump server path, or when the native OT tool must run on the contractor device.
Check Point Enterprise Browser
Contractors reach approved OT assets through the Check Point Enterprise Browser, with least-privilege access and no broad OT network exposure. The native OT tool runs either:
on a jump server you control, or
on the contractor device, with connectivity served through a lightweight Enterprise Browser component
Choose this when no software is allowed on the contractor device and browser-based Zero Trust access is enough.
Check Point SASE Agentless ZTNA
Accessible through any browser with no client required, and no files on the contractor device. Native OT tools run on a jump server you control. Every session is gated by MFA, and you can restrict login access by country and time of day.
PLC HMI Engineering Workstation
Granting third-party contractors access to sensitive OT environments is a demanding problem. It requires strict
security and auditing controls on devices you don't manage, without adding friction for the people using them.
Contractor Remote Access VPN
Broad OT
Exposure
Critical OT Assets
PLC HMI Engineering
Security and Audit Requirements for OT Access
Connecting third-party contractors to sensitive OT environments typically requires:
Strong multi-factor authentication (MFA)
Device posture validation to verify devices meet minimum security standards before granting access
Data control and isolation to prevent sensitive data from being downloaded to the device
Granular, zero-trust access that is restricted to a specific application or jump server, never the broader network
Time-limited connectivity with a built-in workflow that lets contractors request access for a specific task or window
Complete audit and visibility including full session recording
Secure OT Access for Unmanaged Devices
Contractors typically work from an unmanaged laptop, often administered by a third-party IT provider. For that reason,
secure access must be non-intrusive, deployable, and usable on devices the organization doesn't control.
Two approaches fit this need:
Check Point Enterprise Browser
Contractors reach approved OT assets through the Check Point Enterprise Browser, with
least-privilege access and no broad OT network exposure. The native OT tool runs either:
on a jump server you control, or
on the contractor device, with connectivity served through a lightweight Enterprise Browser component
Choose Enterprise Browser when you need
full session governance via a jump server path, or when the native OT
tool must run on the
contractor device.
Check Point SASE Agentless ZTNA
Accessible through any browser with no client required, and no files on the contractor
device. Native OT tools run on a jump server you control. Every session is gated by MFA,
and you can restrict login access by country and time of day.
Choose this when no
software is allowed on
the contractor device
and browser-based
Zero Trust access is
enough.
Secure OT Contractor Access:
Choose the Right Model
Secure OT Contractor Access: Choose the Right Model
Models & comparison
By contrast, remote access VPNs are often unsuitable for OT contractor access, for two key reasons:
Intrusive technology requiring administrative privileges to install, and may intercept all traffic on the device
Network-level access that connects users to the network rather than to a specific application, leading to unacceptable risk
How they compare
Legend: ● Full | ◑ Partial | ○ None
Requirement Enterprise
Browser (Full)
Enterprise Browser (Native App)
Agentless
SASE
Remote Access
VPN
Exposure and access scope
Avoids broad OT network exposure ● ● ● ○
Per-asset least-privilege enforcement ◑ ● ◑ ○
Low lateral-movement risk from contractor
access ● ◑ ◑ ○
Application support
Native OT app on contractor device ○ ● ○ ●
Web, SSH, or RDP access to OT resources ● ● ● ●
Access governance
MFA enforced before access ● ● ● ◑
Just-in-time, time-bound access window ● ● ○ ○
On-premises deployment option ● ● ○ ●
Session control and data protection
Session recording and live oversight ● ◑ ◑ ○
No OT data retained on contractor device ● ○ ● ○
Clipboard, file, and download controls ● ○ ◑ ○
Next step | See which model fits your environment. Talk to your Check Point team.
© 2026 Check Point Software Technologies Ltd. All rights reserved.
Secure OT Contractor Access: Choose the Right Model
Models & comparison By contrast, remote access VPNs are often unsuitable for OT contractor access, for two key reasons:
Intrusive technology requiring administrative privileges to install, and may intercept all traffic on the device
Network-level access that connects users to the network rather than to a specific application, leading to unacceptable risk
How they compare
Legend: Full | Partial | None
Requirement Enterprise Enterprise Browser (Native App) Agentless Remote Access
VPN
Exposure and access scope
Avoids broad OT network exposure
Per-asset least-privilege enforcement
Low lateral-movement risk from contractor
access
Application support
Native OT app on contractor device
Web, SSH, or RDP access to OT resources
Access governance
MFA enforced before access
Just-in-time, time-bound access window
On-premises deployment option
Session control and data protection
Session recording and live oversight
No OT data retained on contractor device
Clipboard, file, and download controls
Next step | See which model fits your environment. Talk to your Check Point team.
© 2026 Check Point Software Technologies Ltd. All rights reserved.
Check Point Enterprise Browser:
Full Governance for OT Contractor Access
Use case OEM contractors need controlled access to OT assets. Native OT tools stay inside your environment. Strong
session governance is non-negotiable.
MFA/JIT Approval
OT Device 1 Web/SSH
Contractor Device
Perimeter Firewall
Enterprise Browser Container
( = just-in-time / time-bound session)
Jump Server
Native App
OT Device 2
Native App
Best for Considerations Regulated OT environments The native OT tool runs one of two ways:
- on a jump server you control, or
- on the contractor's own device with a lightweight
Enterprise Browser component serving connectivity
Strong governance and audit requirements
Just-in-time, time-bound access
Full on-premises deployment
Full session governance including recording, live
oversight, and data controls applies to the jump
server path only
Native OT applications hosted by you, not the contractor
What you get When the native tool runs on the contractor's
device, session recording is limited and OT data
may remain on the device. Use this path when the
native OT tool must run on the contractor's own
device. Confirm supported protocols with your
Check Point team.
MFA before every session
Just-in-time access that expires automatically
Least-privilege access to approved assets only
Minimal network exposure — no broad OT access
Full session recording and live oversight
Clipboard, file, and download controls This model uses the Check Point Enterprise
Browser client, so it is not agentless. When no
software can be installed on the contractor device,
choose Check Point SASE Agentless ZTNA instead.
No OT data left on the contractor device
On-premises deployment option
Native OT tools reached through a jump server you host
© 2026 Check Point Software Technologies Ltd. All rights reserved.
Check Point Enterprise Browser: Full Governance for OT Contractor Access
Use case
OEM contractors need controlled access to OT assets. Native OT tools stay inside your environment. Strong
session governance is non-negotiable.
Contractor Device
( = just-in-time / time-bound session)
Perimeter Firewall Enterprise
OT Device 1
OT Device 2
Web/SSH
Jump Server
Native App
MFA/JIT Approval
Native App
Best for Regulated OT environments
Strong governance and audit requirements
Just-in-time, time-bound access
Full on-premises deployment
Native OT applications hosted by you, not the contractor
What you get MFA before every session
Just-in-time access that expires automatically
Least-privilege access to approved assets only
Minimal network exposure — no broad OT access
Full session recording and live oversight
Clipboard, file, and download controls
No OT data left on the contractor device
On-premises deployment option
Native OT tools reached through a jump server you host
Considerations The native OT tool runs one of two ways:
- on a jump server you control, or
- on the contractor's own device with a lightweight Enterprise Browser component serving connectivity
Full session governance including recording, live
oversight, and data controls applies to the jump
server path only
When the native tool runs on the contractor's
device, session recording is limited and OT data
may remain on the device. Use this path when the
native OT tool must run on the contractor's own
device. Confirm supported protocols with your Check Point team.
This model uses the Check Point Enterprise
Browser client, so it is not agentless. When no software can be installed on the contractor
device, choose Check Point SASE Agentless ZTNA instead.
© 2026 Check Point Software Technologies Ltd. All rights reserved.
Check Point SASE Agentless ZTNA:
Browser-Only Access for OT Contractors
Use case
OEM contractors need browser-based access with nothing installed on their device. OT tools and assets
stay inside your environment.
MFA
OT Device 1 Web/SSH
Best for No software permitted on the contractor device
Browser-only access
Native OT tools that can run on a server or workstation
Controlled access without a full governance program
What you get Fully agentless — nothing installed on the contractor device
MFA before every session
Conditional access based on location and time of day
Low network exposure
No OT application on the contractor device
No OT files on the contractor device
Perimeter Firewall
Jump Server/ Engineering Workstation
OT Device 2
Native App Native App
PLC Access
Considerations
Check Point SASE Agentless ZTNA does not
record sessions on its own. Where session
recording is required, choose the full
Enterprise Browser model, or run the native
tool on a jump server that records sessions
locally.
Per-asset enforcement depends on your
network segmentation.
Native OT tools cannot run on the contractor
device. They run on a customer workstation.
When a contractor must run a native tool
locally under full governance, choose the
Check Point Enterprise Browser model.
Contractor Browser
SASE Portal
© 2026 Check Point Software Technologies Ltd. All rights reserved.
Check Point SASE Agentless ZTNA:
Browser-Only Access for OT Contractors
Use case OEM contractors need browser-based access with nothing installed on their device. OT tools and assets
stay inside your environment.
Contractor Browser
SASE Portal
OT Device 1
OT Device 2
PLC Access
Web/SSH
Jump Server/ Native App
MFA
Native App
Perimeter Firewall
Best for No software permitted on the contractor device
Browser-only access
Native OT tools that can run on a server or workstation
Controlled access without a full governance program
What you get Fully agentless — nothing installed on the contractor device
MFA before every session
Conditional access based on location and time
of day
Low network exposure
No OT application on the contractor device
No OT files on the contractor device
Considerations Check Point SASE Agentless ZTNA does not
record sessions on its own. Where session
recording is required, choose the full Enterprise Browser model, or run the
native tool on a jump server that records
sessions locally.
Per-asset enforcement depends on your
network segmentation.
Native OT tools cannot run on the contractor
device. They run on a customer workstation. When a contractor must run a native tool
locally under full governance, choose the
Check Point Enterprise Browser model.
© 2026 Check Point Software Technologies Ltd. All rights reserved.